A “Set Up Your Passkey” Text From IT? Here’s What to Do
A practical three-step guide for business employees who get an urgent passkey or Microsoft 365 sign-in message.

Microsoft patches record 570 Windows security bugs with two exploited zero days - update now
The July Patch Tuesday Windows update breaks the record for the most security bugs fixed in a single month, with three zero-day flaws and 61 rated critical.

Cyberattacks Are Coming From Inside the Cloud: How Financial Services Should Respond
If it seems like financial services face more cloud-based cyberattacks daily, that’s because they’re using and pushing applications to the cloud more often, according to CrowdStrike’s field CTO for the Americas. Cristian Rodriguez says these cyberattacks tend to start with stolen credentials or identities, allowing adversaries to simply log in and leading to some major data exfiltration events, the deployment of malware or ransomware, and even the use of cloud infrastructure for command and control communications. Sometimes the crime, nation-state or hacktivist groups committing these attacks…

CISA Orders Rapid Patching For ‘Critical’ Ivanti Mobile Management Flaw
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is ordering federal agencies to prioritize patching for a critical-severity Ivanti mobile management vulnerability.

New to VPNs? Everything you need to know about virtual private networks in 2026
Our step-by-step guide covers the many benefits, limited downsides, and everything else you need to know before embracing this popular privacy tool.

Are Businesses Ready to Defend Against AI-Powered Cyberattacks?
The age of artificial intelligence is here, and the effects on cybersecurity will be profound. How profound? In its FutureScape, the tech analyst firm IDC offers a set of predictions on how organizations will use AI to defend themselves in the next year or two, and how threat actors will use it in their attacks. IDC’s Grace Trinidad walked us through the most important and striking of the predictions, including the expectation that breach response playbooks will eventually become dynamic. BIZTECH: How much will security be automated thanks to AI, and how quickly? With AI adoption, security is…

5 Keys to an Effective Cyber Resilience Strategy
Technology is constantly changing and providing new ways for organizations to collaborate more easily and efficiently. However, these advancements also create new opportunities for cyberattacks. Here are a few key things to consider when producing a strong, well-planned strategy for cyber resilience in enterprise businesses. DISCOVER: Here are four security trends to watch in 2026. 1. How Do You Assess the Environment for Vulnerabilities? Identifying and prioritizing risks allows businesses to allocate resources effectively, addressing the most critical vulnerabilities first. Engaging a third…

Financial Services Organizations Need Layered Cybersecurity To Counter Exploitation Trends
Patching known vulnerabilities has always been — and always will be — a foundational requirement for cybersecurity. But new data from SonicWall suggests that financial services organizations must be far more targeted and risk aware in how they approach patch management, while also investing in a layered cybersecurity strategy designed to withstand real-world exploitation. In its 2025 Threat Brief, SonicWall reports that more than 6.9 million threats targeting Microsoft vulnerabilities were blocked by SonicWall firewalls in 2024 — a 110% increase year over year. For banks, credit unions,…

Ingram Micro: Data From 42,000 Individuals Impacted In 2025 Cyberattack
Ingram Micro disclosed that data belonging to more than 42,000 individuals was impacted in connection with the July 2025 ransomware attack that disrupted the company’s online systems for nearly a week.

Top 6 Cybersecurity And AI Predictions For 2026
Among the top cybersecurity and AI predictions for 2026 are a surge in AI-generated vulnerabilities, more-autonomous cyber defense agents and impossible-to-identify deepfakes.

Edge Devices On AWS Infrastructure Targeted By Russian Cyberattacks In ‘Yearslong’ Campaign
AWS cloud infrastructure targeted by cyberattacks from Russian hackers in threat actor campaign focused on customers’ network edge devices.
Secure the Work Anywhere Workforce With Endpoint Security Services
Small businesses have embraced flexible work. Staff can be at home three days a week, then catch a flight to a client site, then answer email from an airport lounge. It’s great for productivity — but every laptop, tablet and phone connecting to company data is a potential point of attack. Today’s work anywhere model means the network perimeter is everywhere and nowhere at once. That makes endpoint security one of the most important layers of protection small businesses can implement. Many devices arrive with built-in security features, but those aren’t designed to protect corporate data…
SMB Cybersecurity: Going Beyond the Basics To Build a Resilient and Scalable Security Framework
Small to medium-sized businesses (SMBs) face increasing pressure to strengthen cybersecurity while maintaining agility and cost efficiency. IT leaders must move beyond reactive defense and toward operationalized maturity — creating systems that are resilient, scalable and audit-ready. Using guidance from the National Institute of Standards and Technology (NIST) Cybersecurity Framework and FINRA’s cybersecurity practices, enterprise-grade security principles can be adapted for use by SMB security leaders. This includes advanced zero-trust implementation and integrating extended detection and…

Cisco, SonicWall Disclose New Attacks Exploiting Zero-Day Flaws
Zero-day vulnerabilities in Cisco and SonicWall products have been exploited in new cyberattack campaigns, the vendors disclosed Wednesday.

How Amazon Is Finding Big Security Benefits From Showing Up To The Office: Analysis
Thwarting insider threats has been a major, if unintended, benefit of Amazon’s return to the office five days a week in 2025, according to Amazon Chief Security Officer Steve Schmidt.
React Server Vulnerability Is No Cause For Panic: Security Expert
A critical-severity vulnerability impacting the popular React open-source library deserves attention, but is far from the apocalyptic scenario that some in the cybersecurity industry are making it out to be, according to well-known security researcher Kevin Beaumont.
The 10 Hottest Cybersecurity Startups Of 2025
Our picks for the hottest cybersecurity startups of 2025 include companies in key categories such as AI security and agentic-powered cyber defense.
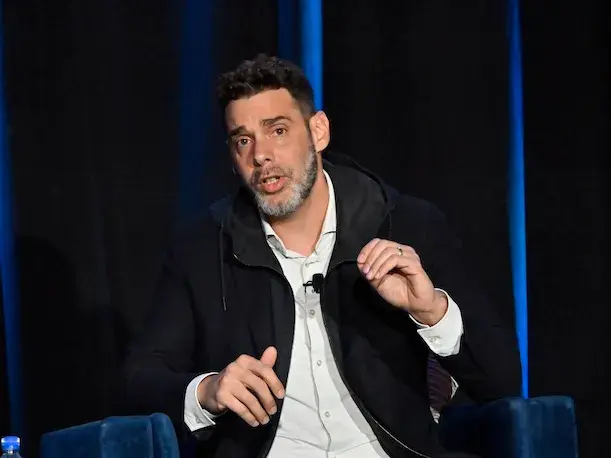
SentinelOne CEO: SIEM, Purple AI Driving ‘Outsized’ Growth Surge
SentinelOne is seeing major contributions from products beyond its core endpoint security offering, underscoring a rise in adoption of the company’s broader Singularity platform by partners and customers, SentinelOne Co-founder and CEO Tomer Weingarten said Thursday.

Mixpanel security incident: what OpenAI users need to know
OpenAI shares details about a Mixpanel security incident involving limited API analytics data. No API content, credentials, or payment details were exposed. Learn what happened and how we’re protecting users.
CISA Urges Quick Fortinet Patches Amid Exploitation Of New FortiWeb Vulnerability
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is urging a quick response to Fortinet’s disclosure of a zero-day vulnerability impacting its web application firewall, FortiWeb, which has been exploited in cyberattacks.
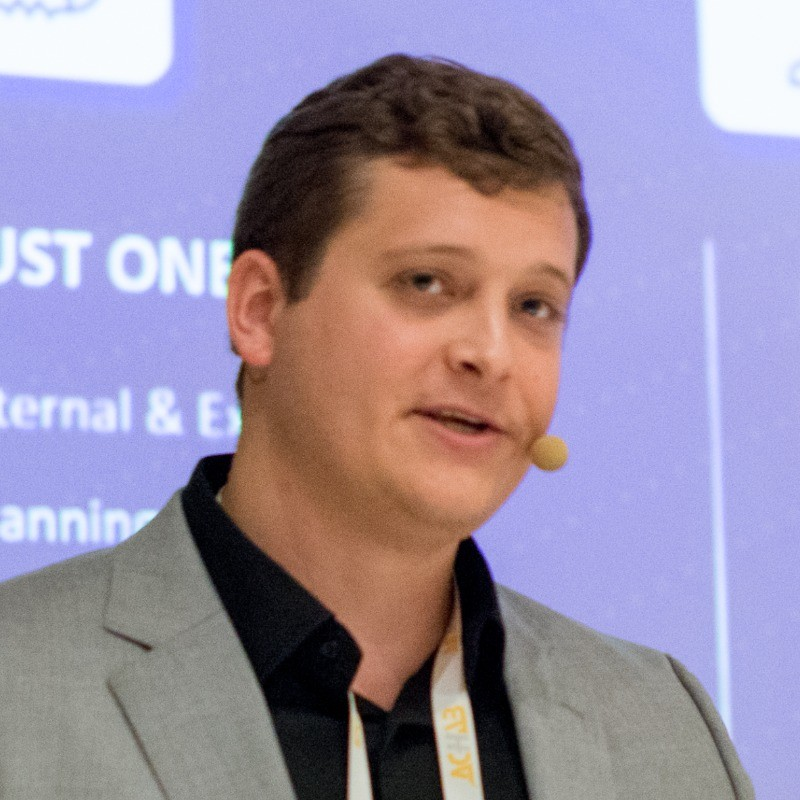
ConnectSecure CEO On New AI Reports For Vulnerability Management: ‘Transparency And Privacy Are Non-Negotiable For Us’
ConnectSecure’s broader goal is to make cybersecurity more accessible for SMBs by giving MSPs enterprise-grade tools.
Protecting Your Business from Cyber Threats
Learn essential cybersecurity strategies to protect your business from evolving digital threats.
Stay Updated with AI & IT Trends
Join over 1,000 IT professionals receiving weekly insights on artificial intelligence, cybersecurity, and emerging technologies.
No spam, unsubscribe anytime. Read by IT leaders at Fortune 500 companies.